Using CAA records with Namecheap
I'm getting tired of having to explain to DNS registrars (and even a DNS registry, once) how DNS works -- knowing this is literally their entire job, and yet this will be my sixth time doing so. But first, some context.
I am the principal administrator of a small IRC network. All of our TLS-related services use certificates from LetsEncrypt, the free and automated Certificate Authority created by the ISRG in the wake of the Snowden revelations of mass unwarranted surveillance.
Further work by ISRG and the IETF in this area includes RFC 7258 (Pervasive Monitoring Is an Attack), which describes the reasonable belief that designing future application protocols to resist this mass surveillance is a Very Good Idea, and RFC 8555 (Automatic Certificate Management Environment), which laid the framework for the process of requesting and installing TLS certificates to become entirely automated, resulting in the mass adoption of effortless HTTPS for all kinds of websites, big and small. This was basically the protocol that people were already using to interact with LetsEncrypt, but it had yet to be standardised. There were some changes, but this is not relevant to this blog post. The publication of this standard allowed other CAs to integrate with this ecosystem with confidence.
The IETF had also realised by this point that permitting any CA to issue certificates for any domain is a Very Bad Idea, so they had also published RFC 6844 (DNS Certification Authority Authorization Resource Record), which is a standard that specifies a DNS record that domain name owners can create to restrict which CAs are allowed to issue certificates for it. This has since been superseded by RFC 8659 (DNS Certification Authority Authorization Resource Record), but that is irrelevant for the purposes of this blog post for reasons I will get into.
For several years now, we have had a CAA record permitting only LetsEncrypt to issue certificates for our domain. However, it was a blanket CAA record, meaning that any LetsEncrypt account could request certificates for any name under our domain name. This is also less than ideal, because anyone can create a LetsEncrypt account in approximately 5 seconds, without supplying or verifying any personal information. To this end, I sought to modify our CAA records to use the accounturi and validationmethods parameters introduced by RFC 8657 (Certification Authority Authorization Record Extensions for Account URI and Automatic Certificate Management Environment Method Binding).
It is important to note that this RFC only describes the specific naming and meaning of these two parameters; it does not introduce support for the parameters themselves. Parameter support has existed since RFC 6844, published over TWELVE years ago.
Context over, this is where my woes begin.
I login to Namecheap's domain administration interface in order to add some new CAA records. As soon as I type the very first semicolon following the CA issuer domain, it errors out, saying that this is an invalid record. The situation does not improve when I add a parameter (even though the syntax described by RFC 6844 does not require a parameter after a semicolon):
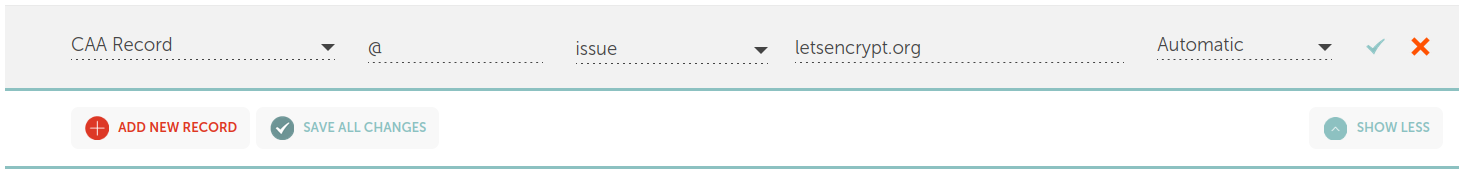
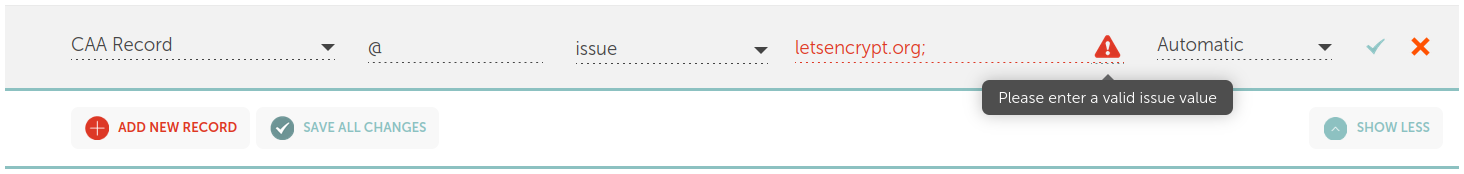
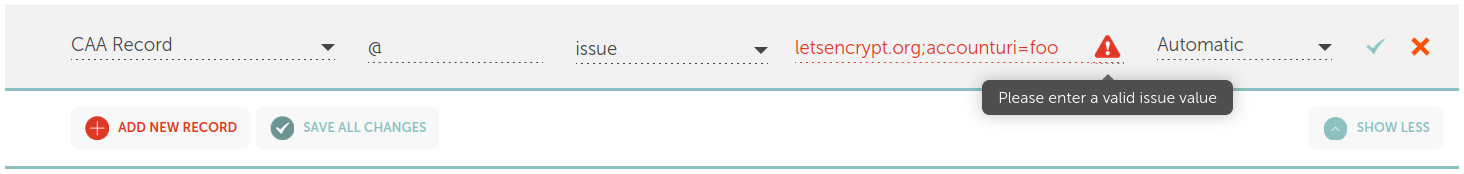
So, I reached out to Namecheap Support. This should be a very simple process, right?
From: Aaron Jones <redacted>
To: support@namecheap.com
Subject: Unable to modify CAA records
Date: Thu, 17 Apr 2025 05:47:17 +0000

Hello.

I write to enquire as to when your DNS records management interface
will properly support CAA records (introduced by RFC 6844 in
January 2013).

I am unable to add any parameters to the "issue" property as prescribed
by section 5.2 and documented at https://letsencrypt.org/docs/caa/ -
your interface insists that these perfectly valid records are anything
but, and the save button does not work.

I am attaching example screenshots.

Regards,

--
Aaron Jones
Network Administrator
The reply arrives approximately 20 minutes later (fantastic), but it is immediately off to an ominous start:
From: Namecheap Domains Support Team <domainsupport@namecheap.com>
Subject: Unable to modify CAA records
Date: Thu, 17 Apr 2025 06:08:49 +0000

Hello,

Thank you for contacting our Namecheap support team!

Unfortunately, the .asc extension is not supported here, so we
can't deal with such files. Supported extensions for chats and
emails: .ca-bundle, .cer, .crt, .csv, .doc, .docx, .eml, .jpeg,
.jpg, .key, .mov, mp4, .p12, .p7b, .p7c, .p7s, .pdf, .pem, .pfx,
.png, .txt, .wav, .xls, .xlsx, .zip.

As for the screenshots, the field marked in red seems to have an
incorrect value. In order for us to check the case further, we
need some additional details. Please specify:

1) Your Namecheap username
2) The Support PIN
3) CAA records in full form that you need to set up
4) Domains in question

We are looking forward to your reply.

-
Best regards,
Namecheap Team
Easy enough. Their ticketing system doesn't understand OpenPGP email signatures, a standard introduced almost 24 years ago by RFC 3156 (MIME Security with OpenPGP). No matter, that isn't relevant to the support request. They also haven't correctly signed off the e-mail with --. No matter, this is hardly the first case of a company that can't correctly send e-mail these days. Note this is meant to be hyphen, hyphen, space, but I can't figure out how to get Markdown to not eat that last space.
I reply thus:
From: Aaron Jones <redacted>
To: Namecheap Domains Support Team <domainsupport@namecheap.com>
Subject: Re: Unable to modify CAA records
Date: Thu, 17 Apr 2025 06:23:41 +0000

On 17/04/2025 06:08, Namecheap Domains Support Team wrote:
> Hello,
>
> Thank you for contacting our Namecheap support team!
>
> Unfortunately, the .asc extension is not supported here, so
> we can't deal with such files.

That's a PGP signature, introduced by RFC 3156 Section 9.2
(August 2001).  You may ignore it.

> As for the screenshots, the field marked in red seems to have
> an incorrect value.

Not according to the syntax section of RFC 6844, nor
LetsEncrypt's own CAA record documentation as linked in my
original e-mail.

> In order for us to check the case further, we need some
> additional details. Please specify:
>
> 1) Your Namecheap username

<redacted>

> 2) The Support PIN

<redacted>

> 3) CAA records in full form that you need to set up

I am attaching this, as it is too long to avoid word wrapping.

> 4) Domains in question

See attached.

> We are looking forward to your reply.
>
> Best regards,
> Namecheap Team

--
Aaron Jones
Network Administrator
I won't bore you with the dozen CAA records that I attached; I will just include the value of the issue property of one of them. They all had the same syntax, just different account identifiers and validation methods. Again I am including only the value of the issue property below, as that is the only important part of this blog post:
letsencrypt.org;validationmethods=dns-01;accounturi=https://acme-v02.api.letsencrypt.org/acme/acct/1280282246If you go ahead and read RFC 6844 Section 5.2 right now, you can trivially determine that this is a valid value for this property.
However, they do not agree. Their reply:
From: Namecheap Domains Support Team <domainsupport@namecheap.com>
Subject: Unable to modify CAA records
Date: Thu, 17 Apr 2025 06:44:29 +0000

Hello Aaron,

Thank you for getting back to us and providing the verification
details.

The error message was received due to the incorrect value pasted
during the record creation.

Please do the following:

- Having logged into the Namecheap account, go to your Domain
  List -> click 'Manage' next to the domain > the 'Advanced DNS'
  tab -> the 'Host Records' section.

- Then click on 'Add New Record' and create the following
  record:

  Type: CAA Record | Host: @ | Tag: Issue |
  Value: letsencrypt.org | TTL: Automatic

- To save the changes, just click on the checkmark on the right.
  Please allow the records at least 30 minutes to propagate.

You may also check the details of the CAA record creation in
this guide:

https://www.namecheap.com/support/knowledgebase/article.aspx/9991/38/caa-record-and-why-it-is-needed-ssl-related/#caa_howto

Please check it on your side and let us know if we can be of any
further assistance.

-
Best regards,
Namecheap Team
Completely missing the point. I didn't paste the value, I wrote the value. Also, DNS propagation is a myth.
I suppose I should be used to this by now. My reply:
From: Aaron Jones <redacted>
To: Namecheap Domains Support Team <domainsupport@namecheap.com>
Subject: Re: Unable to modify CAA records
Date: Thu, 17 Apr 2025 07:08:28 +0000

On 17/04/2025 06:44, Namecheap Domains Support Team wrote:
> Hello Aaron,
>
> Thank you for getting back to us and providing the
> verification details.

No problem.

> The error message was received due to the incorrect value
> pasted during the record creation.

Again, it is not incorrect.  I suggest reading RFC 6844 and
its successor RFC 8659 (November 2019).

In particular, the current edition of the CA/Browser Forum
Baseline Requirements, Section 3.2.2.8, states that certificate
authorities MUST process CAA records in accordance with RFC
8659.

RFC 8659 Section 4.2 describes the "issue" property:

   The CAA issue Property Value has the following sub-syntax
   (specified in ABNF as per RFC5234).

   issue-value = *WSP [issuer-domain-name *WSP]
      [";" *WSP [parameters *WSP]]

   issuer-domain-name = label *("." label)
   label = (ALPHA / DIGIT) *( *("-") (ALPHA / DIGIT))

   parameters = (parameter *WSP ";" *WSP parameters) / parameter
   parameter = tag *WSP "=" *WSP value
   tag = (ALPHA / DIGIT) *( *("-") (ALPHA / DIGIT))
   value = *(%x21-3A / %x3C-7E)

Put simply, this means that a CAA record "issue" property
contains:

- Zero or more leading whitespace characters (ASCII Space 0x20
  and/or ASCII Horizontal Tab 0x09 in any combination and
  amount including none)

- An optional domain name for the certificate authority issuer
  followed by zero or more whitespace characters

- An optional semicolon, followed by zero or more whitespace
  characters, a parameter consisting of a tag, zero or more
  whitespace characters, an ASCII Equals Sign 0x3D, zero or
  more whitespace characters, and a value

- Any further optional parameters repeated as described in the
  previous point

It can be trivially demonstrated that all of the records I
provided to you do satisfy this syntax and are therefore valid.
Your system is unnecessarily rejecting records that certificate
authorities would correctly process, if only you would let them.

> Please do the following:
>
> - Having logged into the Namecheap account, go to your Domain
>   List -> click 'Manage' next to the domain > the 'Advanced
>   DNS' tab -> the 'Host Records' section.

I was already there; that's where my screenshots came from.

> - Then click on 'Add New Record' and create the following
>   record:
>
>   Type: CAA Record | Host: @ | Tag: Issue | Value:
>   letsencrypt.org | TTL: Automatic

We already have a blanket issue CAA record for LetsEncrypt.

I am attempting to restrict it to a specific set of LetsEncrypt
accounts, rather than any LetsEncrypt account as it is set up
currently, as per LetsEncrypt's documentation.

> You may also check the details of the CAA record creation in
> this guide:
>
> https://www.namecheap.com/support/knowledgebase/article.aspx
> /9991/38/caa-record-and-why-it-is-needed-ssl-related/

This documentation is out of date.  For example, it does not
provide examples for LetsEncrypt at all; nor does it provide
examples for the validationmethods and accounturi parameters
introduced by RFC 8657 (November 2019) which I am attempting
to set.

Regards,

--
Aaron Jones
Network Administrator
It then takes them over 30 minutes to reply, instead of the usual 20 minute cadence we've had so far. The reply is appalling:
From: Namecheap Domains Support Team <domainsupport@namecheap.com>
Subject: Unable to modify CAA records
Date: Thu, 17 Apr 2025 07:41:42 +0000

Hello Aaron,

Thank you for getting back to us!

To our regret, we can assist better with SSL certificates
purchased at https://www.namecheap.com/security/ssl-certificates/

We recommend contacting the service provider for better
assistance with your request.

Looking forward to hearing from you.

-
Best regards,
Namecheap Team
SERIOUSLY?
You didn't correctly implement verification of this record's value to begin with, twelve years ago. You then let it languish for the last five years after the introduction of specific standardised parameters. You're completely ignoring what I've explained to you, and now you want us to pay you more money for substandard and incomplete service, when that still won't resolve the issue?
We recommend contacting the service provider for better
assistance with your request.
The service provider is Namecheap. That may soon change; the domain is not mine, but I have poked the owner.
UPDATE:
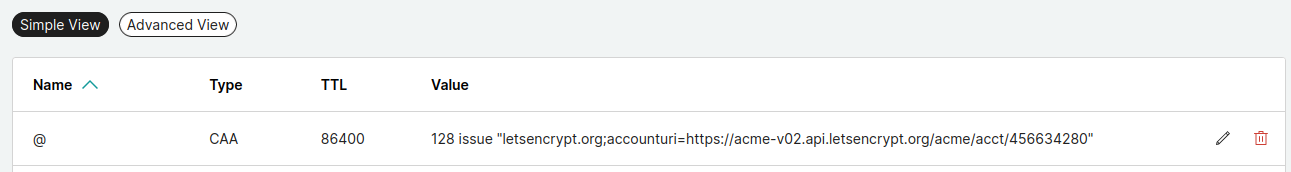
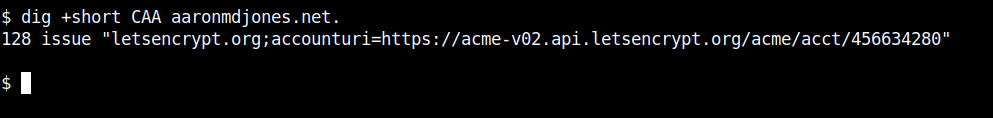
I was able, however, to immediately perform this operation for my own domain name, painlessly, at a different registrar (Gandi LiveDNS):
Would you look at that...